Posts

Linux File Special Permissions - Sticky Bit

Image
This is last of the three series posts regarding Linux special file permissions. We know that in addition to the basic file permission there are three more  special permissions. They are Set User ID (SUID) Set Group ID (SGID) Sticky Bit and in this post will cover Sticky Bit

Linux File Special Permissions - SGID

Image
This is second of the three series posts regarding Linux special file permissions. We know that in addition to the basic file permission there are three more  special permissions. They are Set User ID (SUID) Set Group ID (SGID) Sticky Bit and in this post will cover SGID

Linux File Special Permissions - SUID

Image
In an earlier post we saw different types of basic Linux file permissions. In addition to the basic file permission there are three more  special permissions. They are Set User ID (SUID) Set Group ID (SGID) Sticky Bit

How to change ownership of a file

Image
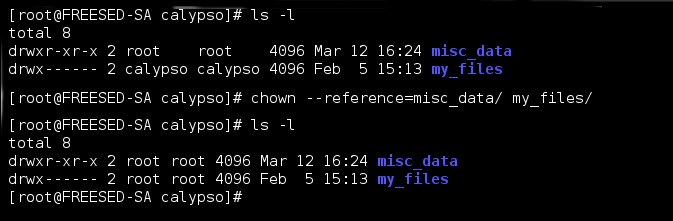
In our previous posts we saw how to change the permission on a file for  different users. Now lets see how to change the ownership of a file. To change the ownership /group ownership of  file or a directory we use chown command. Syntax for chown command is

Basic chmod examples

Image
In our previous post we discussed how to change the permission or mode of a file with chmod command. Now lets see few basic examples regarding how to use chmod via Command Line Interface

How to change the permission of a file in Linux?

Image
In the last post we discussed about the basic file permission. Now lets see how to change the permission of a file or a directory in Linux. To change the access rights we use the chmod command.

Linux File Permissions - Basics

Image
In a multi-user operating system, there will be more than one user account probably handled by different users. What would happen if all the user accounts have permission to access each and every file or command in an operating system? There is a chance for a complete disaster. To avoid such a scenario filesystem has a method to assign access permission to specific system users and groups. The ability of a user to  view, modify and run a particular file or a directory depends upon this access right.